The CISO Who Avoided DLP for 20 Years – and What Finally Changed His Mind
DLP Sucks Live Episode 2 recap: CISO Tal Hornstein explains why he avoided DLP for two decades, what changed with AI, demonstrated by Jazz live in action.
A 20 Year Bet Against DLP – Until Now
For 20 years, Tal Hornstein — now CISO at Cast & Crew and former CIO/CISO at Hippo Insurance and CISO at Globality — made a deliberate choice: no DLP. Not because he didn’t understand the risk. Because the technology wasn’t worth the pain.
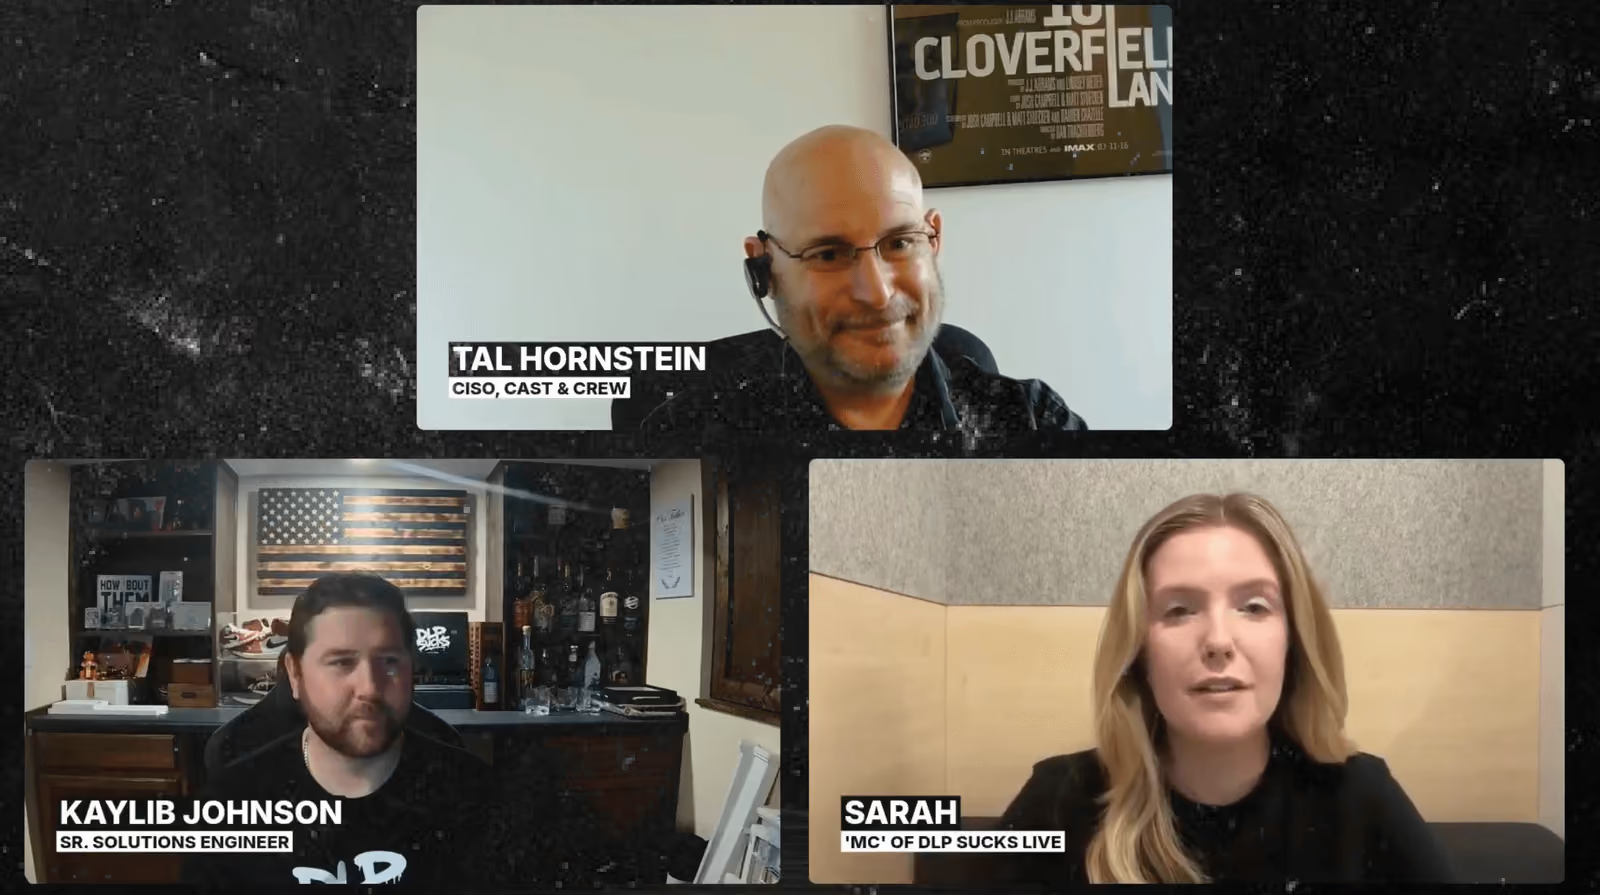
In Episode 2 of DLP Sucks Live, Tal joined Jazz host Sarah Wallek and Jazz Senior Solutions Engineer Kaylib Johnson to explain exactly why, what changed, and what it looks like when DLP actually works.
Quick Answer: Why Do CISOs Avoid DLP?
Traditional DLP tools failed for three core reasons:
- They couldn’t accurately classify unstructured data at scale
- They required constant manual maintenance — often a dedicated FTE — just to manage regex-based policies
- The cost of upkeep rarely justified the risk reduction, so DLP fell off the priority list
Tal’s Case Against Traditional DLP
Tal opened with a framework that cuts right to the core of why DLP historically failed. Effective data loss prevention requires three things to work:
- Data classification — understanding what the data actually is
- Data flow awareness — knowing where data comes from and where it’s going
- Data lineage — tracking ownership, origin, and context over time
The problem? For most of the last two decades, none of these were achievable at the scale or accuracy security teams needed.
“The efficiency of the product just didn’t justify the investment. The cost of maintaining it simply didn’t buy down the risk enough to make it onto my priority list.” — Tal Hornstein, CISO at Cast & Crew
The culprit was regex. Traditional DLP tools forced security teams to build and maintain rules using regular expressions — deterministic, inflexible patterns that had to be precisely calibrated for every data type, every business process, every new use case. Too narrow and you get false negatives. Too broad and you drown in false positives. Either way, you’re paying an FTE to keep refining rules while your business keeps changing beneath your feet.
Kaylib Johnson, who spent years working with ForcePoint and Trellix before joining Jazz, echoed this from the practitioner side. He described watching customers pay for traditional DLP licenses, then never actually implement the product — because they couldn’t figure out how to tune the policies to a workable state.
The Financial Services Problem Is Especially Acute
Sarah asked Tal to speak specifically to financial services organizations, where DLP pressure is highest. His answer was stark.
In financial services, almost every employee has legitimate access to sensitive data. The job is to ensure that data stays in legitimate business use — and never leaks to unauthorized destinations or gets mishandled through flawed processes. That requires observing and understanding data movement at an individual level, across the organization, continuously.
That was simply impossible with pre-AI technology. And the cost of getting it wrong is rising fast. Tal cited data breaches now costing organizations millions to tens of millions of dollars in fines alone — before you account for reputational damage and customer attrition.
“A data leak is now estimated in millions or tens of millions of dollars just in fines, not to speak of reputational loss and the customer attrition.” — Tal Hornstein
What Changed: AI Makes the Impossible Possible
The inflection point, Tal explained, is AI’s ability to do what humans can do intuitively but machines historically couldn’t: understand unstructured data.
Unstructured data — a document, a Slack message, a screenshot, a pasted text block — is easy for a person to read and contextualize. It’s been nearly impossible for a rules-based system to handle reliably. Large language models changed that. AI can now:
- Classify unstructured data with high confidence — without regex
- Observe patterns across large volumes of individual activity
- Make accurate judgment calls on whether data is being handled appropriately
- Identify not just individual incidents, but flawed processes — entire teams or departments that are systematically mishandling data
That last point was Tal’s most important contribution to the conversation. The old model of DLP was reactive: catch the file upload, fire the alert, block the action. The new model is behavioral and systemic. It identifies dangerous patterns before they become incidents.
“Having an AI agent sitting down and looking at what people are doing and understanding the risks they are generating — that’s where the new technology introduces capabilities that never existed before.” — Tal Hornstein
This was the insight Tal brought when he served as an early design partner for Jazz. He pushed for a system that could not just detect events, but quantify and qualify dangerous behaviors — measure the volume of risk being generated, prioritize it, and track whether remediation is actually reducing residual risk over time.
The Live Demo: Three Real-World Scenarios
Kaylib Johnson then demonstrated Jazz’s agentic DLP investigation capabilities live. Three scenarios, each illustrating a different failure mode that traditional DLP misses entirely.
Scenario 1: The Disgruntled Employee
Roy, a business development manager, copies sensitive proprietary pricing models and strategic partnership details from a corporate Notion workspace and pastes them into a personal Gmail account. Traditional DLP might catch a file upload attempt — if the policy was correctly configured. Jazz’s Melody, the Agentic Investigator, produced a plain-English investigation summary: what happened, when, to whom, and why it’s highly indicative of deliberate data exfiltration. The data lineage was fully mapped. The classification was automatic. The investigation took seconds, not hours.
Scenario 2: The Accidental Exposure
Same employee, different intent. Roy copies a JSON configuration block containing internal API credentials from Visual Studio Code and pastes it into a third-party formatting tool (JoFormatter.org) in Chrome. He almost certainly didn’t realize the block contained sensitive infrastructure data. A traditional DLP tool, configured to watch for specific file types or known PII patterns, wouldn’t have caught this. Jazz caught it, classified the API key exposure, and flagged the incident — enabling the organization to understand and respond, not just block and move on.
Scenario 3: Unstructured Data Leaving Through Messaging Apps
Frank, a sales engineer, copies customer contact information and contract details from Salesforce and pastes them into Apple Messages. Kaylib pointed out that standard DLP tools typically can’t monitor messaging apps like Apple Messages or WhatsApp. Once the Salesforce data was copied, it became unstructured — and invisible to most DLP platforms. Jazz tracked the full data lineage: from Salesforce CRM, through Chrome, into Apple Messages, to a specific recipient. Whether the intent was innocent or not, the organization now knows exactly what happened.
Throughout all three scenarios, Melody — Jazz’s Agentic Investigator — delivered human-readable investigation summaries with full context, evidence, data lineage, and next-step recommendations. Security teams can ask Melody follow-up questions directly, or set policies to suppress or block similar events in the future.
Tal’s Advice to CISOs Who’ve Avoided DLP
Sarah closed by asking Tal to speak directly to CISOs who share his history — skeptical of DLP, burned by past implementations, content to deprioritize it.
His advice was direct:
“I totally understand the approach. DLP has failed us. It never worked properly. It was usually too expensive and too inefficient. But I think things have changed profoundly. With this new technology, there is now a way to make DLP worthwhile. My advice would be to take another look — reach out, watch a demo, maybe even do a proof of concept, speak to other people who already implemented solutions such as Jazz.” — Tal Hornstein
Kaylib added a practitioner’s note: the biggest shift isn’t just the technology, it’s the mindset. You no longer need to build and tune policies before you get value. You don’t have to choose between drowning in false positives and missing real threats. The system does the contextual reasoning for you.
Why This Matters in 2026
The risk calculus has shifted. Regulatory pressure around data protection is higher than it’s ever been — from GDPR to CCPA to emerging AI governance frameworks — and the average cost of a data breach continues to climb. Meanwhile, the volume of sensitive data flowing through AI tools and GenAI applications has exploded — Jazz’s own data shows organizations are running an average of 447 GenAI tools per environment, most of them unsanctioned.
Continuing to avoid DLP because traditional tools didn’t work is no longer a defensible strategy. The technology has caught up to the problem. Tal spent 20 years waiting for that to happen. He’s now an advocate of a platform he believes finally got it right.
If you’re a CISO in the same position — skeptical but curious — Jazz is worth a second look.
Watch the Full Episode
Want to see what Jazz would uncover in your own environment? Schedule a demo and find out.